Updated September 17, 2026
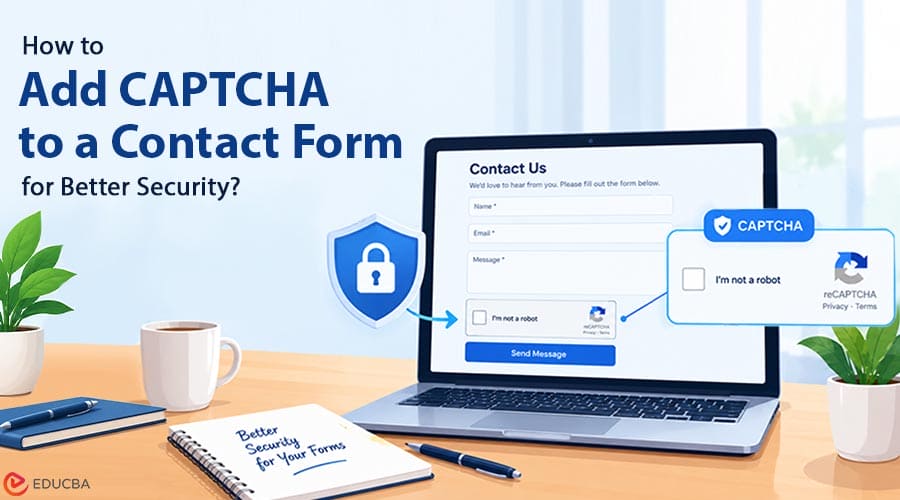
Every contact form on the internet eventually ends up on a bot’s target list. Once that happens, a business inbox fills up with fake inquiries, broken links, and spam offers within days. Adding a CAPTCHA to a contact form is the most common fix, but the setup trips up more site owners than it should. This article walks through the exact steps to add CAPTCHA to a contact form, the CAPTCHA types worth considering, and the mistakes that quietly break forms or hurt conversions once the CAPTCHA goes live.
What is a CAPTCHA and Why a Contact Form Needs One?
CAPTCHA stands for “Completely Automated Public Turing test to tell Computers and Humans Apart.” It is a small challenge placed in front of a form, built to let a human through while blocking automated scripts. A contact form without one is an open door. Bots scan the web for form fields, then submit thousands of fake entries an hour, each one designed to plant spam links, phishing attempts, or junk data into a business’s inbox or database. A properly configured CAPTCHA cuts that traffic to almost zero while adding little to no friction for a real visitor.
Types of CAPTCHA You Can Add to a Contact Form
Different CAPTCHA solutions provide different levels of visibility and protection. Consider the following options before choosing one for your website.
1. ReCAPTCHA v2 (Checkbox)
The visitor ticks “I’m not a robot.” Some visitors also get an image puzzle if Google’s risk score is uncertain. It is the most recognizable option and the easiest to set up.
2. ReCAPTCHA v3 (Invisible)
No checkbox, no puzzle. Google scores each visitor from 0 to 1 in the background, and the site decides what score blocks a submission. It removes friction entirely but needs a bit more configuration on the code side.
3. HCaptcha
A privacy-focused alternative to reCAPTCHA, often chosen by sites that want to reduce dependence on Google’s infrastructure.
4. Cloudflare Turnstile
A lightweight option built for sites already using Cloudflare. It runs a background check similar to reCAPTCHA v3 without a visible widget in most cases.
5. Honeypot Field
A hidden form field invisible to a human but visible to a bot’s script. If the field gets filled in, the submission is silently rejected. It adds zero visual friction and pairs well with one of the options above for extra protection.
Setup Steps to Add CAPTCHA to a Contact Form
Once you have selected a CAPTCHA provider, follow these general steps to integrate it with your form.
1. Choose a CAPTCHA Provider
Pick reCAPTCHA, hCaptcha, or Turnstile based on how much visual friction is acceptable and whether the form already sits inside a Cloudflare setup.
2. Register the Site and Generate API Keys
Every provider requires the domain to be registered first. This step returns two keys, a site key for the front end and a secret key for the back end. The secret key should never be exposed in the page’s source code.
3. Add the Provider’s Script to the Page
This is a small JavaScript snippet placed on the page that hosts the contact form, usually right before the closing body tag.
4. Insert the CAPTCHA Widget Inside the Form
A single div or script tag, depending on the provider, renders the checkbox or badge inside the form itself, using the site key generated earlier.
5. Verify the Response on the Server Side
This is the step most tutorials skip, and most bots exploit. The form’s backend script sends the CAPTCHA token to the provider’s verification endpoint along with the secret key, then only processes the form if that verification returns a success response.
6. Test the Form Across Devices and Browsers
A CAPTCHA that renders fine on desktop Chrome can overlap with other form elements on a small mobile screen, or fail silently in an older browser. A few real test submissions from different devices catch this before real visitors do.
7. Adding a CAPTCHA Through a Website Builder or CMS
Most WordPress contact form plugins, including Contact Form 7, WPForms, and Gravity Forms, have native reCAPTCHA and hCaptcha support built into their settings screen. Pasting the site key and secret key into the plugin’s integration tab handles steps two through five automatically, which is why a WordPress site rarely needs custom code for this.
Common Mistakes When Adding a CAPTCHA to a Contact Form
Knowing how to add CAPTCHA to a contact form is only part of the process. Incorrect implementation can leave the form vulnerable or create unnecessary problems for visitors.
1. Skipping Server-Side Verification
A CAPTCHA that only checks the box on the front end and never confirms the token with the provider’s API can be bypassed by a script that submits the form directly, without ever loading the CAPTCHA widget.
2. Mixing Up the Site Key and the Secret Key
The site key belongs in the page’s HTML. The secret key belongs only in the server-side verification call. Reversing the two breaks the CAPTCHA entirely and exposes the secret key to anyone who views the page source.
3. Forgetting to Update the Key When the Domain Changes
A key generated for a staging domain silently fails once the form goes live on the production domain, since most providers tie a key to a specific set of registered domains.
4. Choosing a CAPTCHA that is Too Aggressive for the Form’s Purpose
A multi-image puzzle on a simple newsletter signup drives real visitors away faster than the spam it blocks. The friction level should match how sensitive the form actually is.
5. Not Adjusting the Score Threshold on reCAPTCHA v3
The invisible version returns a score rather than a pass or fail. A threshold set too low lets bots through; one set too high blocks real visitors who happen to look suspicious to the algorithm, for example, visitors using a VPN.
6. Ignoring Accessibility
A CAPTCHA that only works with a mouse, or that has no audio alternative for a visually impaired visitor, locks out a portion of real, willing customers.
7. Leaving the CAPTCHA Badge Floating Over Other Content
ReCAPTCHA v3’s badge sits fixed in a corner of the page by default, and hiding it without adding the required attribution text violates Google’s terms of use.
8. Never Test After a Theme or Plugin Update
A form’s HTML structure can shift after an update, and a CAPTCHA widget nested in the wrong spot in the DOM can stop rendering without any error message.
How CAPTCHA Setup Affects Page Speed and SEO?
A CAPTCHA script is still a third-party script, and every third-party script adds a small delay to page load. On a contact page that already carries a heavy chat widget or several tracking pixels, an unoptimized CAPTCHA load can tip a page’s Core Web Vitals score in the wrong direction. This rarely matters on a standalone contact page that search engines are not trying to rank, but the same script loaded site-wide, for example on every blog post’s inline lead form, is a different story.
Loading the script asynchronously, and only on pages that actually contain a form, keeps the CAPTCHA’s SEO footprint close to zero. Teams that are not confident auditing this themselves often bring in a specialist instead. SEO boost in Bali runs technical audits that cover exactly this kind of issue, checking how third-party scripts such as a CAPTCHA widget affect Core Web Vitals, page speed, and crawl budget across an entire site rather than just the page it sits on.
Best Practices for a Frictionless CAPTCHA Experience
- Default to the least visible option that still stops the spam a site is actually seeing. Most low-traffic sites do fine with a honeypot field alone.
- Load the CAPTCHA script only on pages with a form, not site-wide.
- Monitor form submission volume for two weeks after launch. A sudden drop in legitimate submissions usually means you need to adjust the threshold or friction level.
- Keep a fallback contact method, such as an email address, visible somewhere on the page in case a legitimate visitor gets blocked.
Final Thoughts
A CAPTCHA is a small piece of a contact form, but it is one of the few pieces that decides whether the inbox behind that form stays usable. Learning how to add CAPTCHA to a contact form can help reduce automated spam and keep business inquiries manageable. Choosing the right type for the form’s risk level, verifying the response on the server side, and testing across devices before launch covers most issues. Once the CAPTCHA is live, keep an eye on both the spam it blocks and the real submissions it might be filtering out.
Frequently Asked Questions (FAQs)
Q1. Does a CAPTCHA slow down my website?
Answer: A CAPTCHA script adds a small amount of load time, usually under a fraction of a second when loaded asynchronously and scoped to only the pages that need it.
Q2. Which CAPTCHA is best for a small business contact form?
Answer: reCAPTCHA v3 or a honeypot field covers most small business needs without adding visible friction. A visible checkbox is worth adding only if spam continues after the invisible option is in place.
Q3. Can a CAPTCHA be bypassed?
Answer: Yes, if server-side verification is skipped. A properly verified CAPTCHA is much harder to bypass, though no CAPTCHA blocks 100% of automated traffic.
Q4. Does law require a CAPTCHA?
Answer: No specific law requires a CAPTCHA. Some privacy regulations require disclosure when a third-party script such as reCAPTCHA collects visitor data, which is why a privacy policy update usually accompanies the setup.
Q5. Do I need a developer to add a CAPTCHA to my form?
Answer: Not on most CMS platforms. A WordPress site using a plugin like Contact Form 7 or WPForms needs only the site key and secret key pasted into the plugin’s settings. A custom-built form usually needs a developer for the server-side verification step.
Recommended Articles
We hope this guide on how to add CAPTCHA to a contact form helps you strengthen your website’s security and reduce unwanted submissions. Check out these recommended articles for more insights and practical strategies to improve your website’s performance and user experience.